
Shadow IT: The Invisible Security Threat Lurking in Your Network

Shadow IT: The Invisible Security Threat Lurking in Your Network
You cannot secure what you cannot see. In the realm of endpoint security, visibility is the currency of control. Yet, many organizations operate with a false sense of security, unaware that a significant portion of their digital estate remains hidden from their management tools.
This phenomenon is Shadow IT, and it represents a growing blind spot in modern cybersecurity strategies.
We have made it easy for you to find exactly what you are looking for, click on the links below, and jump to a section that interests you.
Shadow IT Examples | Shadow IT risks | Shadow IT policy | Blind spots | Mitigating Shadow IT Security Risks
What is Shadow IT? Definition and Meaning
Shadow IT refers to the use of information technology systems, devices, software, applications, and services without explicit IT department approval.
Employees typically introduce these tools to boost productivity, yet the outcome is a fragmented IT environment where the security team lacks oversight. In the context of endpoint security, this most commonly manifests as Shadow Applications: software installed by users or running as “portable” executables that bypass standard deployment channels.
Shadow IT Examples
To understand the scope of the problem, consider common examples of Shadow IT found in corporate environments:
- Portable Applications: Software that runs directly from a file (e.g., .exe) without a formal installation process. Because these do not register in the “Add/Remove Programs” list, traditional inventory tools often miss them.
- Unmanaged Productivity Tools: Employees downloading PDF converters, file compression tools, or AI plugins directly from vendor websites to bypass ticket queues.
- Cloud Storage & Sharing: The use of personal Dropbox, WeTransfer, or Google Drive accounts to move corporate data.
Shadow IT Risks: The Cost of Blind Spots
The presence of Shadow IT in cyber security introduces critical vulnerabilities that undermine even the most robust perimeter defenses.
1. The Unpatched Attack Surface
Unmanaged software is rarely updated. Shadow IT risks stem primarily from the fact that if IT does not know an application exists, they cannot patch it. With unpatched vulnerabilities remaining a primary entry point for cyberattacks, every piece of Shadow IT represents a critical open door, that must be closed.
2. Regulatory Non-Compliance (NIS2)
The NIS2 Directive establishes requirements for structured vulnerability management and risk handling across digital assets deployed organization-wide. To meet these requirements, organizations must be able to scan and identify the vulnerable status of applications operating within their environment — not just those you actively manage.
Any vulnerabilities found must be addressed and reported to avoid the harsh monetary and non-monetary penalties associated with non-compliance. Because Shadow IT remains unseen by conventional tools, it represents a critical gap in this mandatory vulnerability handling process.
Addressing this gap requires improved visibility into unmanaged executable applications. Solutions designed for this purpose must clearly define their supported detection scope.
Managing the Risk: What is a Shadow IT Policy?
While software tools are essential for detection, security starts with governance. To effectively manage these risks, organizations must establish a clear framework for software usage.
But what is a shadow it policy?
A Shadow IT policy is a set of guidelines that defines how employees can procure, install, and use technology within the organization. Rather than a blanket ban, which can stifle innovation and efficiency, a modern policy should focus on:
- Clear Approval Processes: A simple, fast method for employees to request new tools so they don’t feel forced to go “underground” to do their jobs.
- Acceptable Use: Defining which categories of software (e.g., file sharing, AI tools) are strictly prohibited due to data leakage risks.
- Regular Audits: Stating that the IT team reserves the right to scan for and remove unapproved software to ensure compliance.
However, a policy is only effective if it can be enforced. A rule written on paper offers no protection if you lack the visibility to see when it is broken.
The Blind Spot: Why Microsoft Intune Is Not Enough
Many organizations believe they are covered because they use Unified Endpoint Management (UEM) systems like Microsoft Intune.
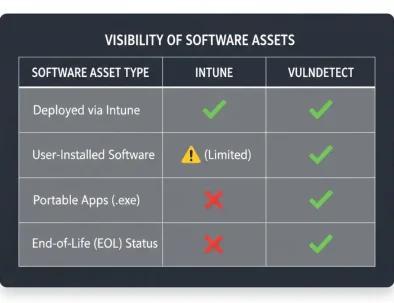
However, Intune primarily reports on the applications it has deployed. It is generally blind to software installed by users outside of the Company Portal or portable applications that do not trigger standard installation logs.
This creates a dangerous gap: Your Intune dashboard may show “All Green” compliance, while vulnerable, unmanaged software operates undetected in the background.
Mitigating Shadow IT Security Risks with VulnDetect
To secure the modern workplace, you need an independent source of truth. VulnDetect serves as this “ground truth,” reducing blind spots by scanning the endpoint itself rather than relying solely on deployment logs.
1. Intelligent Shadow IT Detection
VulnDetect’s lightweight agent scans the endpoint to identify unmanaged and non-Intune-deployed applications within its supported detection scope, including portable apps and executables covered by our detection rules. This provides Shadow IT meaning in a practical sense: turning unknown risks into a known inventory.
VulnDetect focuses on unmanaged executable applications and portable software within its supported rule set. Browser extensions and unsupported application types are outside the current detection scope.
2. Automated Remediation & Blacklisting
Once Shadow
IT is detected, VulnDetect empowers you to act.
- Detect: comprehensive inventory of detected unmanaged applications within your supported application landscape.
- Blacklist: Use persistent jobs to automatically uninstall unauthorized or dangerous software.
- Patch: If the software is legitimate but unmanaged, VulnDetect can take over updates to ensure it remains secure.
3. Verified Supply Chain Security
To guarantee secure software deployment, we ensure that every package is fully verified. By validating SHA256 checksums and AuthentiCode signatures and testing in the EU, we ensure that only safe, trusted software reaches your network.
Reveal Your True Attack Surface
Shadow IT security is not about locking down employees until they cannot work; it is about having the visibility to manage risk intelligently. By combining Microsoft Intune with VulnDetect, you bridge the gap between “managed” and “secure,” ensuring that no application goes undetected.
Schedule a demo to scan your network.