
Securing with Microsoft Intune: Eliminating the Blind Spots in Your Endpoint Management

Securing with Microsoft Intune: Eliminating the Blind Spots in Your Endpoint Management
Microsoft Intune has become the cornerstone of modern device management. However, while it is a powerful tool for administration, relying on it alone often leaves critical security gaps. To achieve true software vulnerability management and meet modern compliance standards like NIS2, you need to look beyond standard features.
We have made it easy for you to find exactly what you are looking for. Click on the links below to jump to a section that interests you:
What is Microsoft Intune? | Key Features & Capabilities | The Limitations of Microsoft Intune | How SecTeer Closes the Gaps | FAQ
What is Microsoft Intune?
Microsoft Intune is a cloud-based service that focuses on (UEM). But what is Intune used for exactly? It allows organizations to control how their devices are used, including mobile phones, tablets, and laptops, ensuring that corporate data remains protected.As a vital part of the endpoint Microsoft ecosystem, Intune software ensures that employees can work securely from any location while IT maintains control over the applications they use.
Key Microsoft Intune Features and Capabilities
When evaluating intune capabilities, several core features stand out:- Automated Deployment: Deploying apps and configurations to devices wirelessly.
- Compliance Policies: Setting rules (e.g., password complexity, encryption) that devices must meet to access data.
- Data Protection: Isolating personal data from corporate data on “Bring Your Own Device” (BYOD) setups.
- Inventory Management: Keeping track of hardware and managed software.
What are the Limitations of Microsoft Intune?
While Microsoft Intune is an industry-standard for device management, it is not a “silver bullet” for cybersecurity. To achieve true cybersecurity risk assessment and NIS2 compliance, IT leaders must address three primary gaps where Intune falls short:
1. The Visibility Gap: What Intune Can’t See
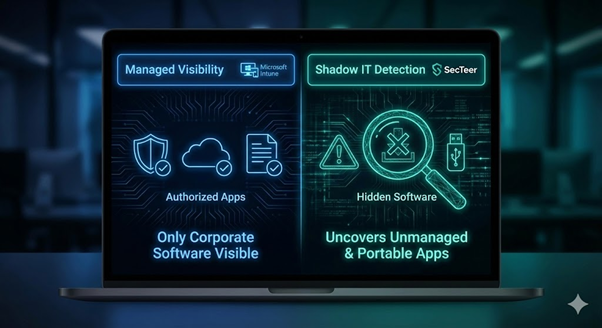
The biggest disadvantage of Intune is that it is fundamentally designed to manage what it has deployed. It provides excellent telemetry for “managed” assets, but it is often “blind” to:
- Unmanaged Software: Applications deployed through scripts, manual installs, or other deployment tools rather than through Intune.
- Portable Apps: Standalone .exe files that run without a traditional installation process.
- Shadow IT: Software that bypasses corporate procurement and IT oversight. If your security strategy relies solely on Intune, your attack surface is likely much larger than your reports suggest. You cannot secure what you cannot see.
2. Operational Complexity & Fragmented UI
As noted in many technical reviews, Intune has a steep learning curve. The administrative interface is extensive and can feel fragmented, often split between legacy and newer portals. For IT teams, this leads to:
- Configuration Risks: A high probability of misconfiguration in compliance policies.
- Operational Chaos: Time wasted navigating complex menus rather than responding to active threats.
- Sync Latency: Reporting is not real-time; it can take hours or even days for a device’s status to update, which is a major hurdle for automated compliance reporting.
3. The Hidden Liability: Closing the 3rd Party Verification Gap
While Intune manages Microsoft updates effectively, third-party patching remains a significant hurdle. Many organizations try to solve this by using external catalogs, but this introduces a new risk: Lack of Verification. Without SHA256 checksums and AuthentiCode signatures, you risk deploying compromised code into your environment.
For a deeper look into the specific operational challenges of 3rd party patching within the Microsoft ecosystem, read our detailed analysis here.
How SecTeer Closes These Gaps
SecTeer doesn’t replace Intune; it strengthens compliance alongside it.
- VulnDetect provides the Shadow IT Detection Intune lacks, revealing your true attack surface through curated scanning.
- PatchPro injects 100% verified, EU-tested packages directly into your Intune environment, ensuring that your Secure Software Deployment is based on trust, not crowdsourced guesswork.
Reveal Your True Attack Surface
Microsoft Intune is an excellent foundation, but SecTeer provides the visibility and automated precision needed to stay secure in a complex threat landscape. By combining Intune’s management power with SecTeer’s vulnerability intelligence, you eliminate blind spots and ensure a Secure Software Deployment process.
FAQ
Accordion Content
It manages and secures your organization’s devices and apps from the cloud, ensuring that only compliant devices can access sensitive corporate information.
Standard Intune is primarily designed to track software it has deployed itself. It often struggles to provide visibility into unmanaged “Shadow IT” or portable applications installed by users.
SecTeer adds a layer of curated detection to find unmanaged software and provides a library of verified, pre-tested 3rd party patches that are automatically injected into your Intune environment.
Microsoft Intune has a steep learning curve and a fragmented user interface. This administrative complexity often leads to operational friction and increases the risk of security misconfigurations that can leave endpoints vulnerable.